The Future CRO: What the Role Looks Like in 2030
In this article
At a glanceA technologist who governs, not a governor who understands technologyA strategic partner, not a risk reviewerA resilience architect, not a framework custodianA voice on ESG and geopolitical risk, not a bystanderWhat stays the sameBoardroom questionsContinue readingAt a glance
A forward-looking perspective on the CRO as a technology governor, strategic partner and resilience architect, grounded in judgment and organizational trust.
When I started in banking risk in Bahrain, the CRO role barely existed as a formal function. Risk was reviewed, not led. The idea that a Chief Risk Officer would sit at the executive committee table, report directly to the board, and hold meaningful authority over how the institution deployed capital was, in most regional banks, still a decade away.
Thirty-five years later, the CRO role has become one of the most consequential in banking. And it is about to change again, more fundamentally than most people in the role are yet prepared for.
By 2030, the CRO who succeeds will look meaningfully different from the CRO who succeeds today. Not because the fundamentals of risk management will change, sound judgment, organizational trust, and the courage to say difficult things will remain as important as they have always been, but because the environment in which those fundamentals are applied will be transformed. The institutions that understand this transformation now and build toward it will have CROs who strengthen their resilience and competitive position simultaneously. The ones that don't will find themselves with a risk function that is perpetually behind the curve it is meant to be managing.
This is my view, built from 35 years of experience and 14 articles in this series, of what the future CRO will need to be.
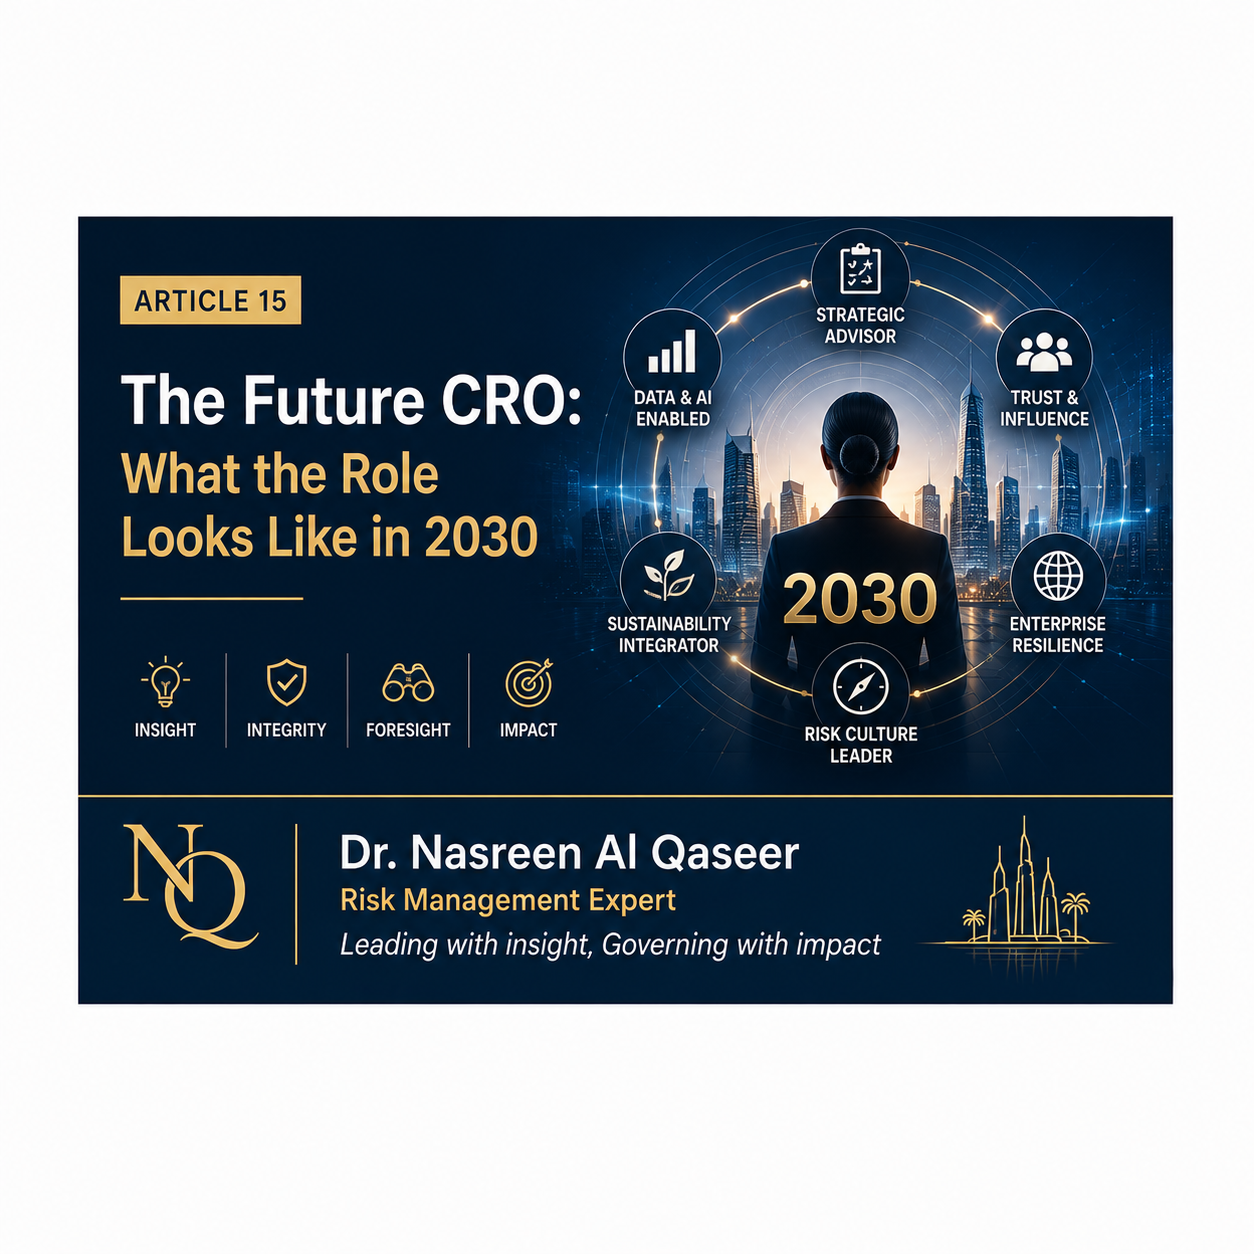
A technologist who governs, not a governor who understands technology
Every article in this series has touched, in some way, on the intersection of technology and risk. AI in credit monitoring. Model risk governance. Cyber risk. Fintech partnerships. Liquidity risk in a digital environment. Operational resilience in an era of digital dependency.
The pattern across all of them is the same: technology is not changing the edges of risk management. It is changing the centre. By 2030, the majority of material risk decisions in a bank will either be made by a model, shaped by a model, or monitored by a model. That makes the CRO's relationship to technology not a competency to develop at the margins but a core part of the role itself.
The future CRO does not need to be a data scientist. But they need to be fluent enough in how models work, where they fail, and how they should be governed to provide genuine oversight rather than deference. They need to understand AI explainability not as a technical concept but as a governance requirement. They need to be able to ask the question that the model builder won't volunteer: what does this model not capture, and what happens when it encounters something it wasn't trained on.
The institutions that get this right will have CROs who treat technology governance as a first-order responsibility. The ones that get it wrong will have CROs who rely on their technology team to tell them what the models are doing, which is not oversight. It is delegation without accountability.
A strategic partner, not a risk reviewer
The most significant evolution in the CRO role over the next five years will not be technical. It will be positional. The CRO who sits downstream of strategic decisions, reviewing what has already been agreed commercially and approving what cannot be stopped, has already lost most of their effectiveness. By 2030, that model will be visibly inadequate.
The future CRO is in the room when strategy is being set, not when it is being presented for approval. They understand the competitive environment, the institution's growth agenda, and the capital allocation choices being considered well enough to shape those conversations rather than react to them. They translate risk appetite from a document into a genuine constraint that informs which opportunities the institution pursues and which it walks away from.
This requires a different kind of CRO capability than the one most risk functions have traditionally developed. It requires commercial literacy alongside risk expertise. It requires the ability to speak the language of the CEO and CFO, not just the language of the risk committee. And it requires the organizational credibility that comes from a track record of being right more often than not, and of adding value to strategic conversations rather than simply slowing them down.
A resilience architect, not a framework custodian
The third transformation is in how the CRO thinks about their primary output. The traditional answer to “what does the CRO produce” is a risk framework: policies, limits, monitoring systems, reporting. Those remain necessary. They are no longer sufficient as a definition of the role's value.
The future CRO thinks of their primary output as institutional resilience, the capacity of the institution to absorb shocks, adapt to changing conditions, and continue serving customers and stakeholders through disruption. That framing changes what the CRO pays attention to. It means thinking about culture as seriously as capital, because a risk culture that doesn't hold under pressure will undermine a capital framework that looks adequate on paper. It means thinking about operational resilience as seriously as financial resilience, because by 2030, the most material disruptions to banking institutions are as likely to come from a cyber incident, a third-party failure, or an AI model that behaves unexpectedly as from a credit cycle turning.
The resilience architect doesn't just measure risk. They build the organization's capacity to withstand it, and they measure their own success not only by whether the institution stayed within its risk appetite but by whether it emerged from stress stronger than it entered.
A voice on ESG and geopolitical risk, not a bystander
Two of the articles in this series, on ESG and climate risk and on geopolitical risk, pointed to the same structural problem: these risks are material, they are growing, and the risk function's ownership of them is, in most GCC institutions, incomplete. By 2030, that incompleteness will be increasingly difficult to sustain.
The future CRO owns the integration of climate risk into credit assessment, stress testing, and portfolio management. They do not leave it in a sustainability function that produces its own metrics on its own reporting cycle. They own the scenario analysis that tells the board what the institution's portfolio looks like under specific geopolitical stress scenarios. They do not leave geopolitical risk as a background condition managed at the compliance layer.
This is not additional scope for its own sake. It is a recognition that by 2030, the boundary between these emerging risks and the core credit, market, and operational risks that the CRO has always owned will be increasingly difficult to draw. The CRO who has built the capability to manage them will be more valuable, more credible, and more effective than the one who has left them to adjacent functions.
What stays the same
Across all of this transformation, three things will not change, and I want to end there because I think they are the most important things I've learned in 35 years.
The first is that organizational trust remains the foundation of everything. A CRO with no organizational trust cannot influence what actually happens in the institution, regardless of how technically sophisticated their framework is. Trust is built slowly, through consistency, through being right more often than not, and through the courage to say difficult things clearly and early. Nothing about the digital transformation of banking changes that.
The second is that the hardest part of the job will still be being heard when it matters. The pressure to move quickly, to approve the deal, to hit the target, will remain. The CRO's value is not in eliminating that pressure but in ensuring it is resisted when the risk is genuinely unacceptable. That requires a combination of courage and judgment that no model will replicate.
The third is that the risk function exists to make the institution stronger, not to make it smaller. The CRO who is remembered, who builds something that lasts beyond their tenure, is not the one who said no the most often. It is the one who helped the institution pursue opportunity wisely, build genuine resilience, and navigate difficulty with its integrity intact.
That has been true for all 35 years I have spent in this profession. I believe it will be true in 2030. And I believe it will still be true long after that.
To everyone who has followed this series, engaged with these ideas, and pushed back where you disagreed: thank you. The conversation is the point. I look forward to continuing it.
Boardroom questions
- Is the CRO involved while strategy is being formed?
- What capabilities must our risk function build for 2030?
- How do we assess resilience, influence and organizational trust?